Features

Everything a defender needs -
in one console.

Scan your Wi-Fi and local network, then extend into detection, forensics, intelligence, response and reporting - a single workflow with zero telemetry.

Live event log

Every event, as it happens - tamper-proof.

A live feed of all activity observed on the wire or read from a host. Each event is tagged with its severity, module, origin and MITRE ATT&CK mapping, with live statistics and full-text search across the stream.

  • Every event with severity, module & ATT&CK mapping
  • Live statistics and full-text search across all events
  • Tamper-proof - nothing leaves the machine
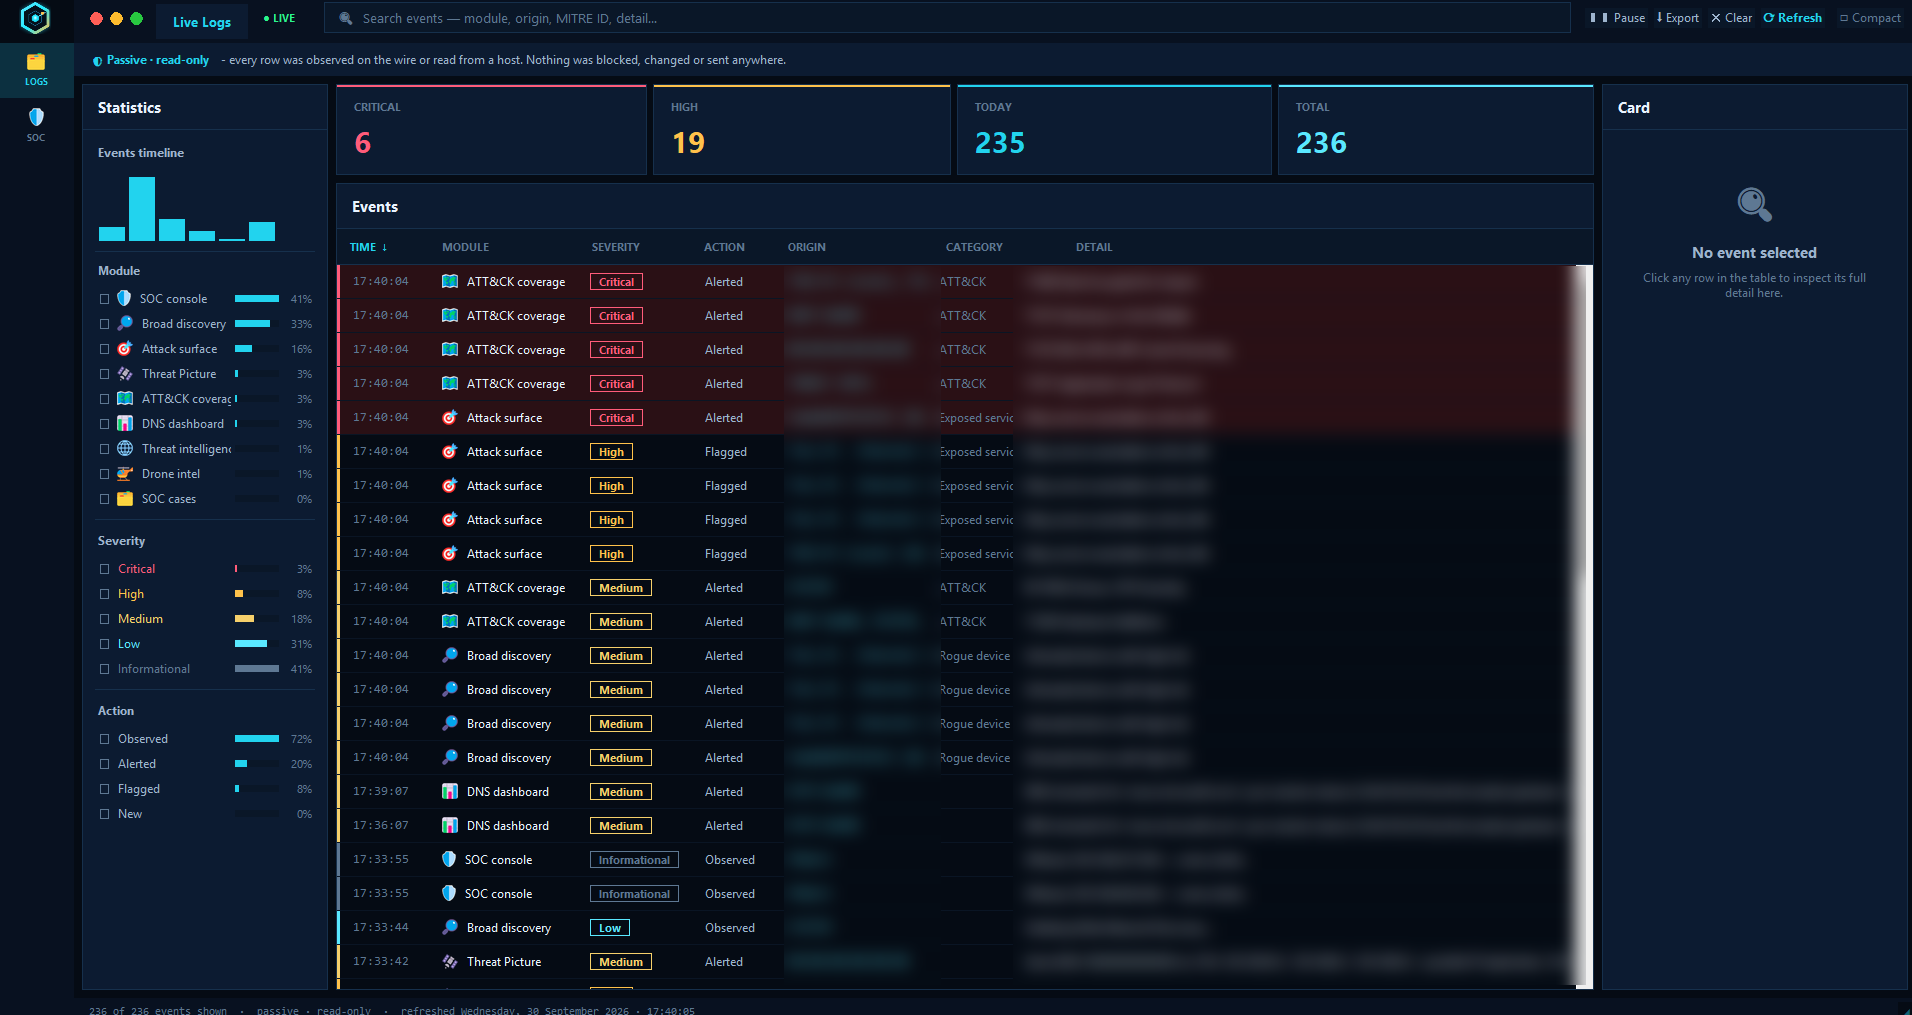
Live event log - every observed event with severity, module and ATT&CK mapping (data redacted)
SOC war room

Your whole operation on one screen.

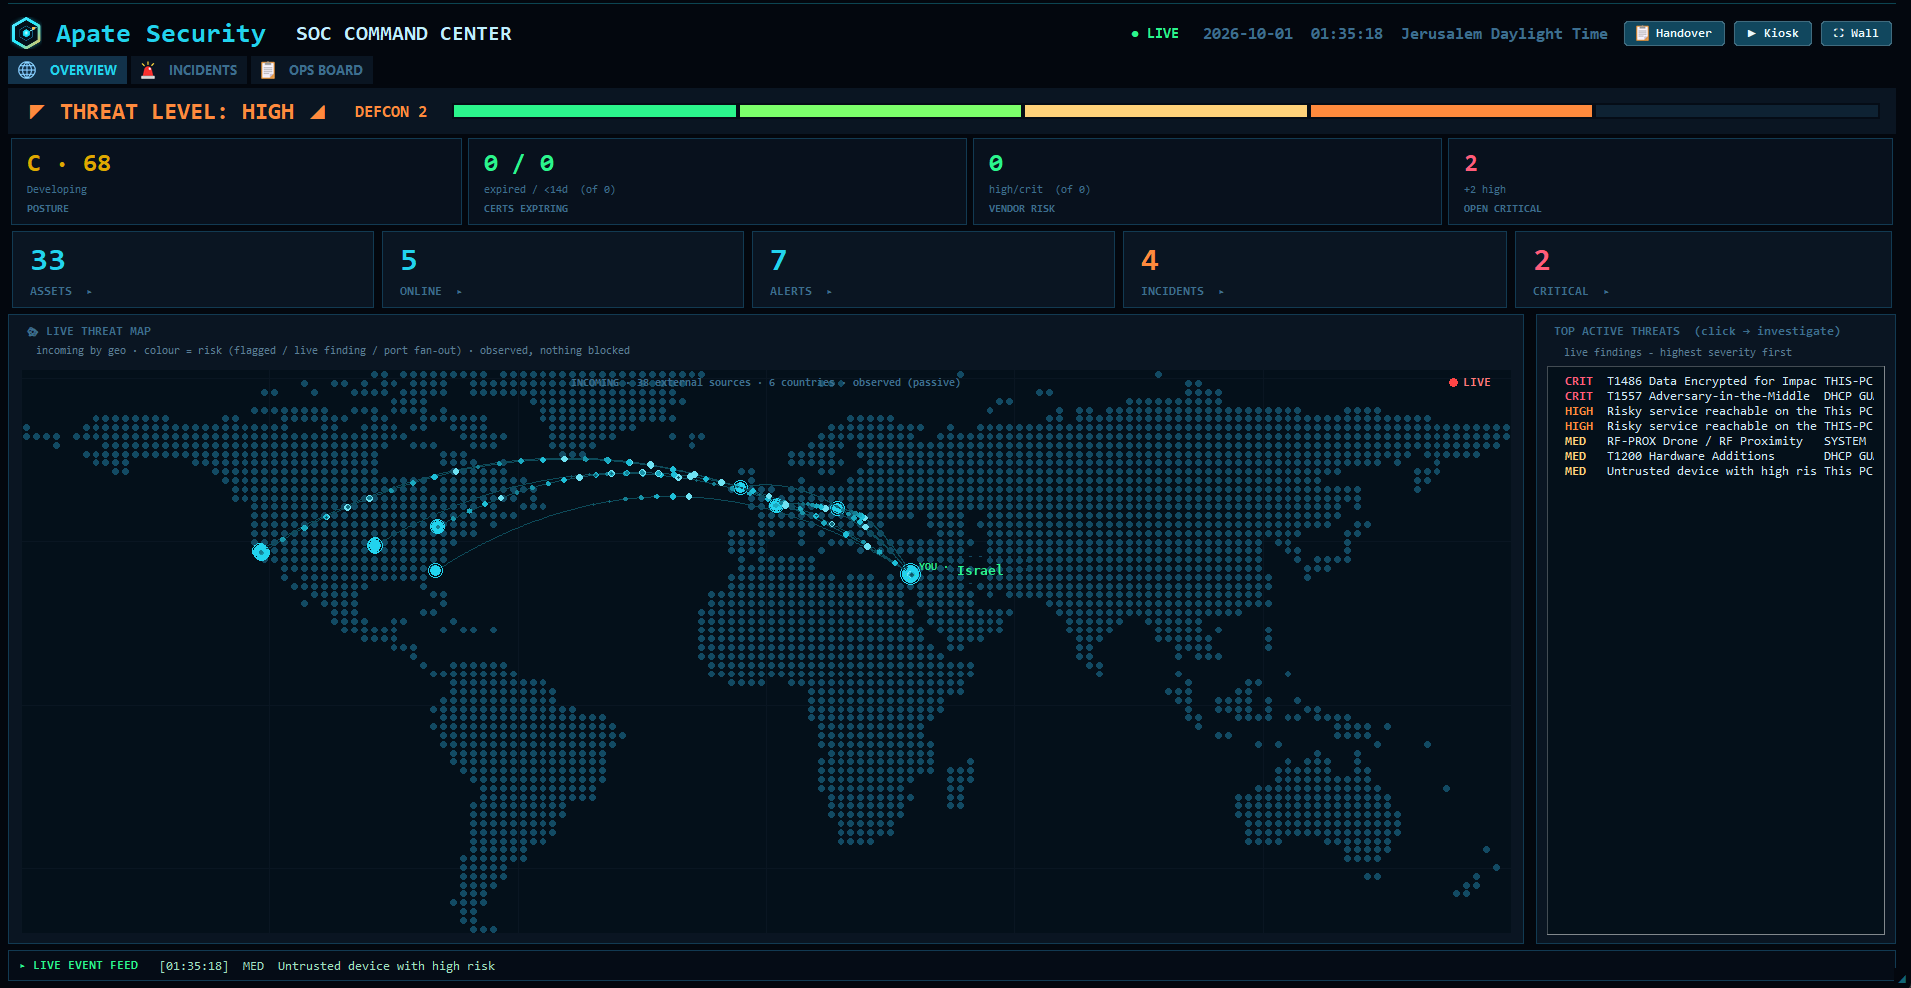
The SOC war room consolidates live alerts, network posture and prioritized risks into a single operational view - so analysts can focus on what matters first and respond quickly, entirely from observed signals.

  • Live alerts & incident triage in one place
  • Network posture and prioritized risk at a glance
  • Built on observed signals
SOC command center - live global threat map, alerts & prioritized risks (data redacted)
See where a link leads

Check any link - without ever opening it.

Paste a suspicious or shortened link and Apate Security resolves the full redirect chain to the real destination in an isolated, disposable sandbox - no cookies, no profile, and your real browser and identity are never exposed. It scores the link for phishing, brand impersonation and malware, and can render a safe, masked preview of the page.

  • Unmasks shorteners & follows every redirect hop
  • Flags impersonation, phishing lures & risky TLDs
  • Safe preview in a headless sandbox - nothing runs on your machine
  • The link is never opened in your browser

Why do the links look broken? On purpose. URLs are shown defanged - http→hxxp and .→[.] - so they can't be clicked or auto-linked. It's a standard safety convention for handling malicious links, not a typo.
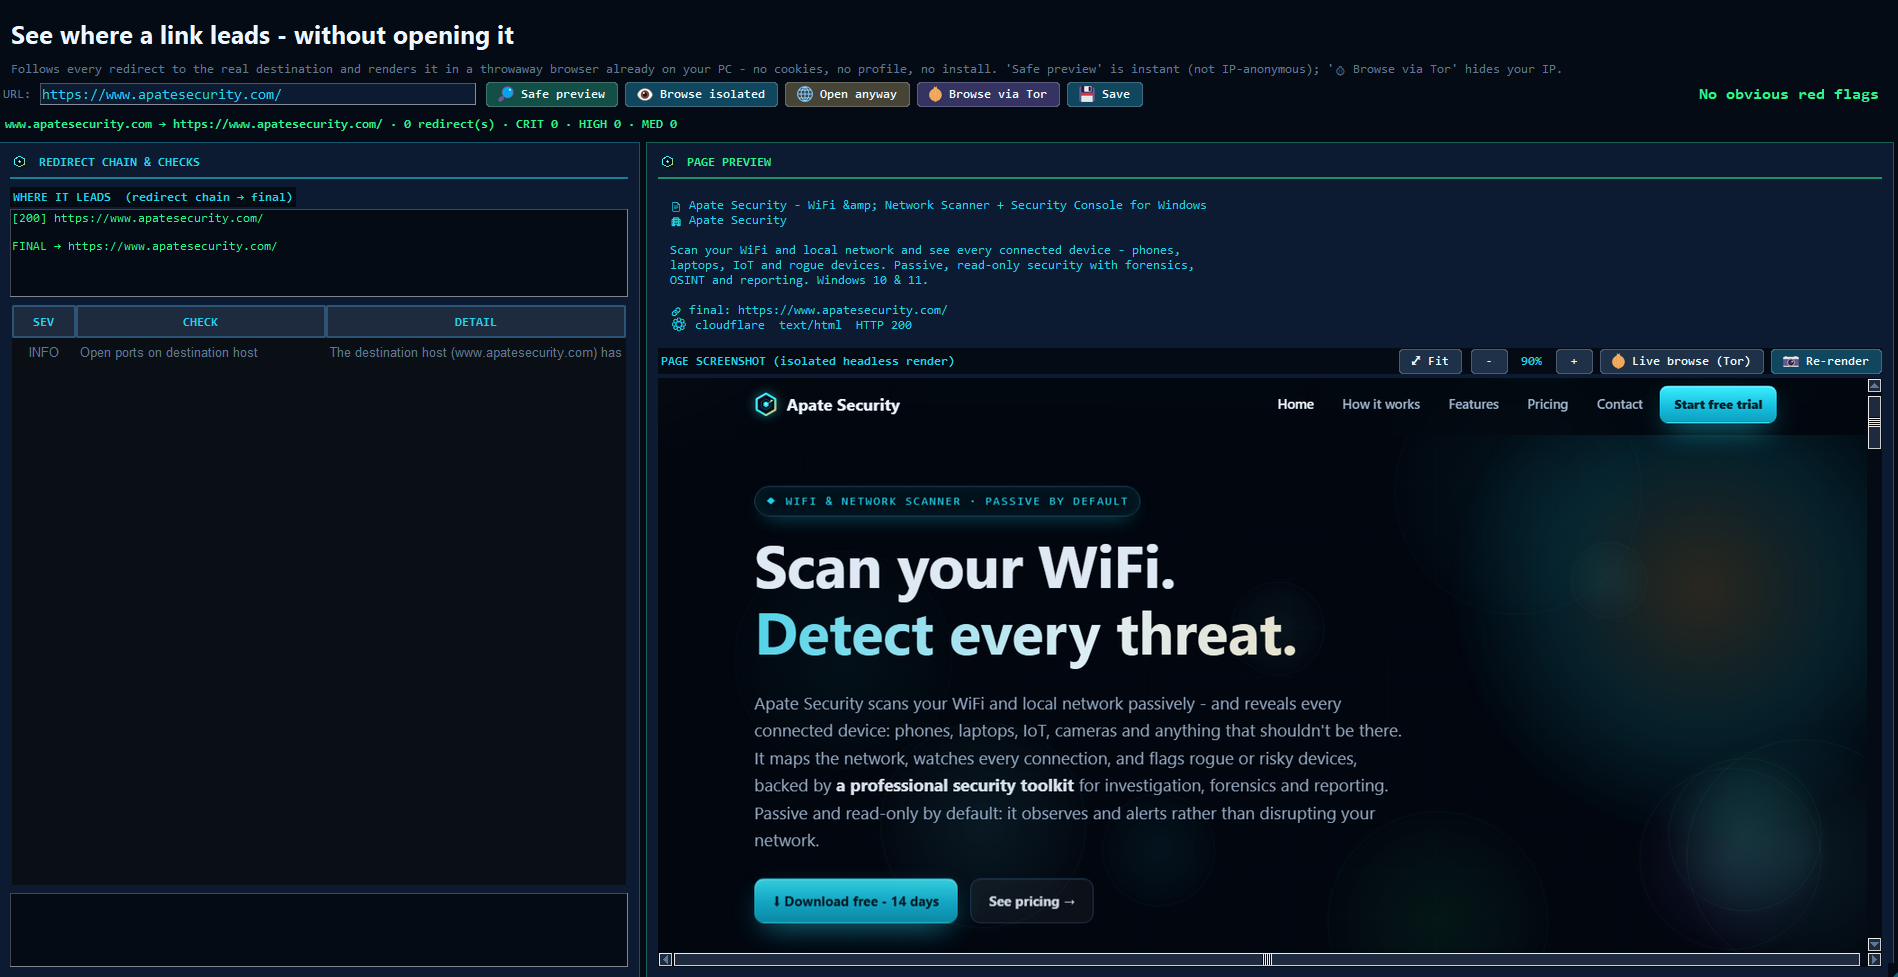
Safe Link Inspector - resolves a link's real destination and scores it, without opening it
Airspace & space

See satellites overhead - and drones in your airspace.

Track satellites passing over your location from public NORAD TLE data, receive drone Remote-ID broadcasts, monitor RF events, and fuse network, RF and Remote-ID data into a single situational picture. Receive-and-compute only - nothing is ever transmitted.

  • Satellite tracker - azimuth/elevation sky plot & passes (public TLE)
  • Drone Remote-ID detection & RF-event monitoring
  • Multi-source threat fusion into one track
  • Receive-only · no telemetry
Satellite tracker - satellites overhead by azimuth/elevation from public TLE
How it compares

One console. No gaps.

Active scanners, antivirus and the router app each leave a gap. Apate watches the whole network continuously and fills them all.

  Apate SecurityAll-in-one console Active scannersProbe-based AntivirusEndpoint agent Router appISP / mesh
Sees every device on the network✓✓✗~
Safe for fragile IoT / OT devices✓✗✓✓
No agents to install on every device✓✓✗✓
Flags rogue APs & evil-twin Wi‑Fi✓~✗✗
Runs on locked-down, managed PCs✓✗✗-
Nothing leaves your network - no cloud, no telemetry✓~✗~
Continuous live monitoring, not one-off scans✓✗~✗

✓ built‑in  ·  ~ partial / limited  ·  ✗ not designed for it  ·  - not applicable

See the full comparison →

And a lot more

Built for real operations

🌍

Live maps

Global threat map, ATT&CK live heatmap and attack-path graphs.

🎯

Threat hunting

Prebuilt hypotheses, beaconing/C2 detection and lateral-movement hunts.

🔬

Forensics & DFIR

PE analysis, Windows Event/Sysmon, PCAP, email & document forensics.

🔭

OSINT toolbox

WHOIS, breach checks, username footprint, EXIF, crypto & dork builder.

☁

Cloud & AppSec

CloudTrail, IAM audit, K8s/Docker linting, IaC & bucket exposure.

📊

Reporting & GRC

CISO briefings, client PDFs, SIEM export and CIS/NIST/ISO mapping.

🔔

Alerting

Send findings to Slack, Teams, webhook or email - your endpoints.

⚙

SOAR-lite

Rules that trigger safe actions and scheduled reports.

🛡

Private by design

No telemetry, no cloud, no destructive scans - safe to run anywhere.

🌐

Multilingual

Interface in English, Русский and 中文; the built-in AI assistant replies in English, Русский or 日本語 - switch anytime.

Threat detection

Catch the behaviors that signatures miss.

Analytics over DNS, flows and TLS metadata surface the moves an intruder makes after they're in - shrinking dwell time and acting as a force-multiplier for a lean SOC.

📶

Beaconing / C2

Timing-regularity (jitter) analysis flags periodic call-outs to command-and-control, even over encrypted channels.

📤

Data exfiltration

Outbound-volume anomalies highlight destinations receiving far more than they send - a classic exfil signature.

↔️

Lateral movement

Internal traffic on admin ports (SMB, RDP, WinRM) that deviates from baseline - the tell-tale of an attacker moving.

🧬

Malware fingerprints (JA3)

Observed JA3/TLS fingerprints matched against offline threat-intel feeds - malware families identified without decryption.

🛰️

DNS tunneling & DGA

Entropy and length analysis on DNS queries catches data smuggled over DNS and algorithmically-generated domains.

🔎

Recon & scanning

A host touching many ports or peers in a short window is surfaced as internal reconnaissance.

Compliance & reporting

Evidence auditors accept - and a story the board understands.

📋

Audit-ready inventory

A continuously-maintained asset and service inventory - the artifact almost every framework asks for first.

🌍

Data-flow & geo mapping

Where traffic goes, by country and ASN - supporting privacy, data-residency and third-party review.

🧭

Framework mapping

Findings mapped to NIST, ISO 27001, PCI DSS and GDPR-relevant controls, ready to hand to an assessor.

📊

Executive risk reporting

A single posture score and trend, in board-ready reports that help a CISO prioritize budget.

Who it helps

Value for every seat in the room.

🎖️

CISO & leadership

A defensible posture score, board-ready reporting and a clear view of exposure to prioritize spend.

🛰️

SOC & analysts

Early detection and a full investigation timeline - scope and root cause established in minutes.

🧑‍💻

Network & IT ops

A live inventory and topology, plus drift alerts when the network changes underneath them.

📑

GRC & compliance

Continuous inventory, data-flow maps and framework mapping - audit evidence that stays ready, not assembled under deadline.

🏭

OT / plant engineers

Visibility into industrial segments, designed to minimize the risk of interference with sensitive equipment.

🤝

MSSPs & consultants

One collector across many client sensors, with branded, per-engagement reporting.

Works where others can't

Built for the networks nobody else can touch.

Because it's self-contained, Apate runs in the places active scanners and cloud tools simply can't go.

🔒

Locked-down corporate PCs

Runs on managed, GPO-restricted Windows machines - no network changes, port mirroring or endpoint agents to get started.

✈️

Air-gapped & offline

No cloud and no phone-home, with offline machine-locked licensing - made for isolated and sensitive environments.

🏭

Fragile OT / ICS networks

Lightweight and low-impact - built to run beside PLCs, medical and industrial gear that aggressive active scans can crash.

Scope & limits

Honest about the boundaries.

Being clear about what Apate does and doesn't do is part of the product - so there are no surprises in a pilot.

🧾

Metadata, not payloads

It analyzes fingerprints and metadata; it does not decrypt content or capture files, packets or credentials.

📍

Coverage follows the sensor

It sees traffic that crosses a monitored point. Org-wide coverage comes from placing sensors at the gateway, core and key segments.

🚫

No endpoint agent

There's no host state (installed software, local files) except what can be inferred from the network - by design.

🛡

Active modes are opt-in

Active and on-path modes are opt-in and off by default - you decide what runs on your network, and when.

See it live

Put it on your network today.

14-day free trial of live network discovery & device inventory - no card required. The full toolkit unlocks with a paid plan.